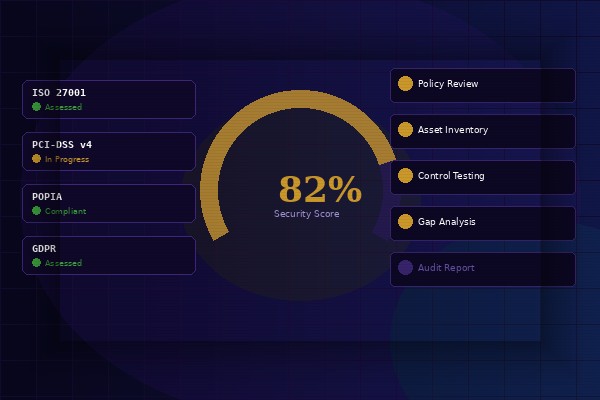
Security Readiness Programmes
Know your posture.
Before attackers do.
Structured, AI-assisted security assessments and automated audit programmes — benchmarked against leading frameworks and built to produce actionable, compliance-ready findings.
📋
What We Assess
- →ISO 27001 ReadinessGap analysis against ISO 27001:2022 controls — clause-by-clause, with remediation priority matrix
- →PCI-DSS ComplianceScoping, gap assessment, and evidence preparation for PCI-DSS v4.0 requirements
- →POPIA & GDPR ReadinessData governance assessment with focus on personal information handling obligations
- →Microsoft Secure Score OptimisationSystematic improvement of Microsoft Secure Score with implementation guidance and tracking
- →Security Architecture ReviewEnd-to-end review of security controls, identity posture, network segmentation, and detection coverage
🤖
Automated Audit Reports (Professional SOC Tier)
- →Continuous posture monitoringAutomated security audit reports produced on a scheduled basis — monthly or quarterly — and reviewed by our security team before delivery
- →Evidence chain includedEvery finding backed by specific log entries, Defender alerts, and configuration snapshots
- →Executive and technical variantsBoard-level executive summary alongside technical detail for your security team
- →Trend trackingPosture improvement tracked over time — demonstrate security investment value to stakeholders
- →Regulatory-ready formatReports structured for regulatory submission, cyber insurance requirements, and auditor review
Ready to understand your
true security posture?
Automated audit reports are included in the Professional SOC tier, or available as standalone engagements.